The CSE Appointment Needs a Public Trust Ledger
Canada’s most sensitive cyber-intelligence post deserves more than a résumé announcement.
Prime Minister Mark Carney announced on September 3 that Scott Jones, President of Shared Services Canada, will become Chief of the Communications Security Establishment after Caroline Xavier’s upcoming retirement. That is not a minor staffing notice. CSE describes itself as Canada’s national cryptologic agency, providing the federal government with information-technology security and foreign signals intelligence. The person at the top of that agency sits at the intersection of cyber defence, secret intelligence, government technology and public trust.
Jones’ official biography includes serious cyber credentials. It lists previous CSE roles as Head of the Canadian Centre for Cyber Security from 2018 to 2021, Deputy Chief for IT Security from 2016 to 2018, Deputy Chief for Corporate Services from 2015 to 2016, and earlier cyber-defence and signals-intelligence systems posts. Those facts matter. This is not an argument that Jones lacks experience.
But the same official biography also lists a politically sensitive bridge in his record: from 2021 to 2022, Jones was “Federal Lead, Proof of Vaccine Credentials” at Immigration, Refugees and Citizenship Canada. From 2022 to 2023, he was Executive Vice-President of Shared Services Canada and concurrently Associate Deputy Minister of Public Services and Procurement. Since September 2023, he has led Shared Services Canada. Now he is moving from federal digital-service delivery and pandemic-era credential work into the agency responsible for foreign signals intelligence and government IT security.
That combination demands receipts. Pandemic credential systems were sold as limited, necessary and controlled. National-security agencies ask for public confidence on exactly the same terms: trust the mandate, trust the safeguards, trust the internal screens. Conservatives should reject the idea that trust is enough. If Ottawa wants Canadians to accept this appointment without suspicion, it should publish the accountability ledger that makes suspicion unnecessary.
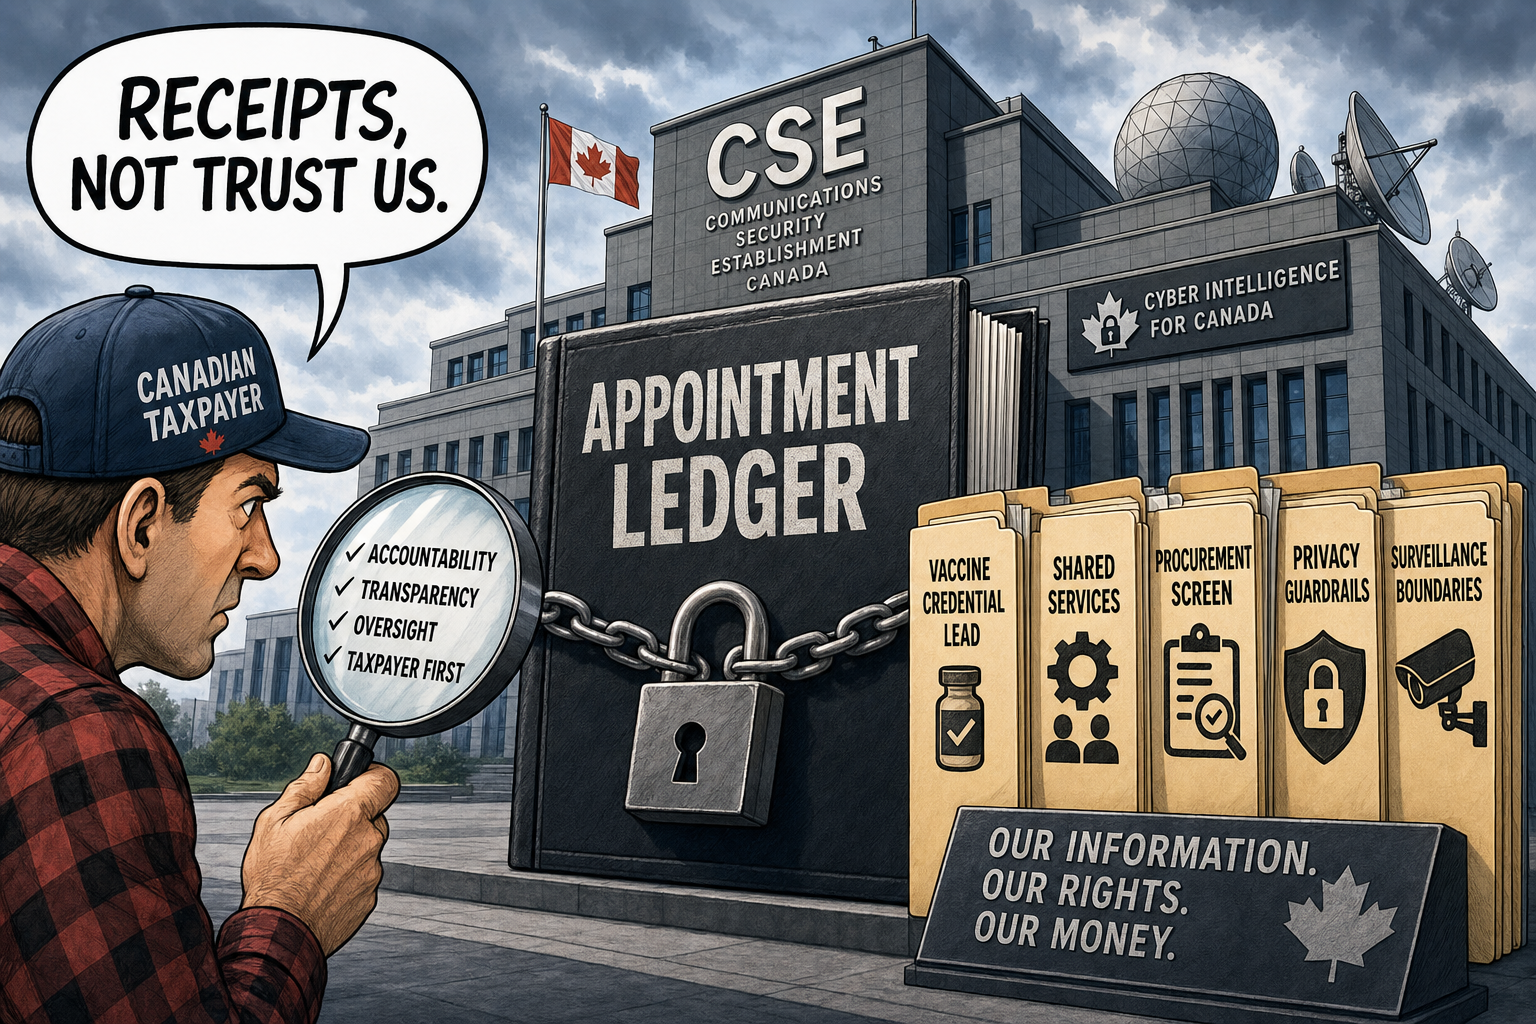
The ledger should include the selection criteria for the CSE chief role, the conflict-of-interest and procurement screens applied to a former Shared Services Canada president, any recusals tied to vendors or departmental technology files, the privacy lessons drawn from federal proof-of-vaccine credential work, and the surveillance-boundary commitments that will guide the new chief. It should also identify what parliamentary, ministerial and review-body briefings will occur before and after the transition.
CSE’s listed minister is the Minister of National Defence, David J. McGuinty. That means the responsibility does not end with a PMO press release. National Defence should be prepared to explain how the appointment strengthens cyber security while protecting Canadians from mission creep, data overreach and procurement opacity.
A government that centralizes digital power and intelligence power owes the public more than biographies. It owes a paper trail. Publish the appointment ledger, the privacy guardrails, the conflict screens and the oversight timetable. If the appointment is as sound as Ottawa says, the receipts should strengthen it.
- Prime Minister of Canada: Prime Minister Carney announces changes in the senior ranks of the public service — September 3, 2026
- Prime Minister of Canada: Scott Jones biographical note — September 3, 2026
- Communications Security Establishment Canada: CSE mandate and minister page
This article does not claim Scott Jones is unqualified. It argues that a CSE appointment involving prior vaccine-credential, digital-service and procurement responsibilities should come with public privacy, conflict-screen and oversight receipts.